Merlyn Consult | Cybersecurity & Risk Management
A few years ago, the cybersecurity conversation was largely about detection. Today, I believe we need to put much greater emphasis on prevention—especially in manufacturing and operational technology (OT).
Artificial intelligence is changing the speed and scale at which cyber threats can be discovered and exploited. While AI also helps defenders, attackers can use automation to search for exposed services, analyse weaknesses and accelerate parts of their operations.
For industrial businesses, the stakes are especially high: a cybersecurity incident can affect not only information, but also production, safety, delivery performance and business continuity.
The reality inside manufacturing environments
Walk through a manufacturing facility and you are likely to find a complex mix of modern production lines, legacy PLCs, SCADA systems, industrial PCs, robots, sensors and custom-built integrations. Equipment from different vendors may have operated reliably for ten, fifteen or twenty years.
That reliability is valuable—but it also makes change difficult. Unlike a typical office IT environment, production equipment cannot always be patched, restarted or replaced on demand. Updates may require vendor approval, testing and scheduled downtime. Operational continuity and safety must remain central to any security plan.
How AI changes the threat landscape
AI-enabled tools can help attackers automate reconnaissance, refine malicious content and process large amounts of technical information. This does not make every cyberattack instant or effortless, but it can lower the barrier to some activities and increase the pressure on organisations with exposed systems.
Defensive strategies therefore need to combine timely detection with stronger architecture, disciplined access management, asset visibility and practical incident preparation.
Are we solving the right problem?
It is understandable that organisations invest in more monitoring, dashboards and alerts. Detection is essential, and well-designed monitoring can identify suspicious behaviour early. Yet adding tools without reducing underlying exposure may create more complexity and alert fatigue.
A prevention-led approach does not replace detection. It complements it by reducing opportunities for attackers and limiting the consequences of a compromised system.
Reduce exposure before an attack
Every attack has an entry point or pathway. Industrial organisations should know which assets and services are reachable, who can access them and which connections are truly required. Unnecessary internet exposure should be eliminated, and access to critical environments should be restricted and monitored.
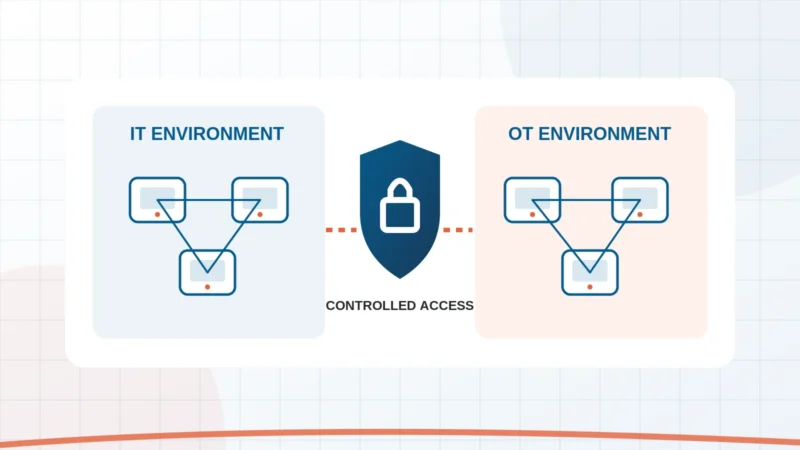
IT/OT network segmentation, secure remote-access gateways, multifactor authentication where feasible and strict vendor-access controls can substantially reduce risk. Segmentation can also help contain an incident before it disrupts an entire production site.
What effective prevention looks like
- Maintain an accurate inventory of OT assets and critical network connections.
- Identify and eliminate unnecessary external exposure.
- Use segmentation and tightly controlled access between IT and OT zones.
- Protect remote access, including connections used by suppliers and integrators.
- Plan safe patching, compensating controls and incident recovery with operations teams.
- Continuously monitor for threats that preventive measures cannot eliminate.
A realistic objective is to make critical systems harder to discover and access—not to promise that any system is literally invisible or impossible to compromise.
Why NIS2 matters
Across Europe, the NIS2 Directive increases attention on cybersecurity risk management, governance, supply-chain security and incident handling for organisations within its scope. Management bodies of covered entities have specific responsibilities under the Directive. Exact obligations and effective implementation depend on the relevant national law, sector and organisational circumstances.
Compliance is important. But the objective should go beyond meeting minimum requirements: protecting safe and reliable operations.
Cybersecurity is becoming a business strategy
Cybersecurity is no longer only an IT responsibility. For manufacturers and logistics operators, a serious incident can affect revenue, delivery commitments, customers and reputation.
My take: prevention and detection belong together
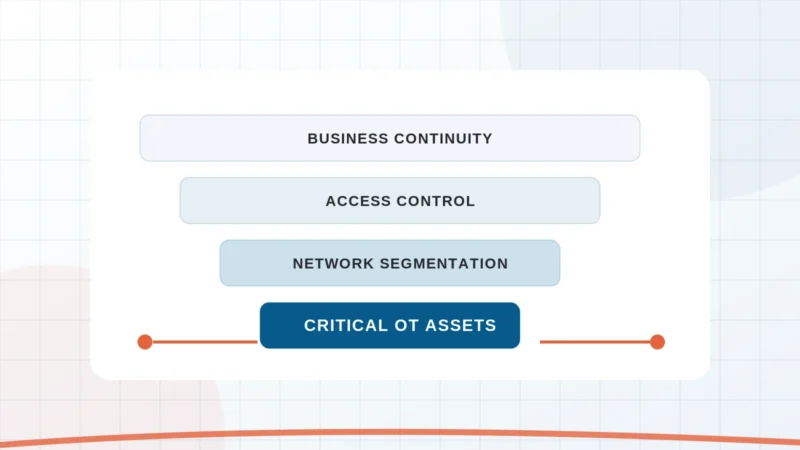
As AI capabilities continue to evolve, simply adding more detection tools will not be enough. The most resilient organisations will combine a clear view of their assets with exposure reduction, controlled access, strong segmentation, monitoring and tested response procedures.
Good OT cybersecurity is not about buying the largest number of tools. It is about making sensible, risk-based decisions that protect industrial operations.
Are manufacturers placing enough emphasis on prevention? I would be interested to hear how other organisations are approaching this balance.
Let’s connect
If you are responsible for manufacturing, OT, industrial automation, cybersecurity or digital transformation, I would be happy to exchange ideas about reducing exposure, preparing for NIS2 and strengthening operational resilience.
No sales pitch. No obligation. Just a professional conversation about safer and more resilient industrial operations.
Connect on LinkedIn